
Segmentation Initial setup
Best Practice: ON (default)
- Turn on Segmentation early
- Segmentation has caveats, please check release notes and with SE
- The following only work in the default segment: 9.5 and lower versions
- IPV6
- Branch NAT (Fix 9.6)
- Multicast
- Overlapping IP space - requires Branch NAT
- BGP/OSPF - Supported in all segments
-
Always check release notes for caveats
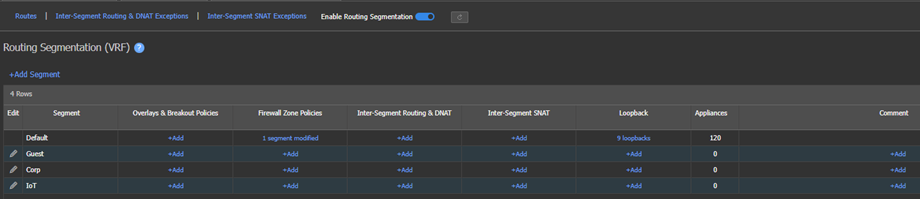
Segmentation has both VRF and Template zone-based firewall. Do not apply a firewall policy via templates with segmentation enabled.
Do not apply a Templated ZBFW security policy via templates with segmentation enabledThe system is designed around one policy. Having two policies can get very confusing and require a lot of administrative overhead.
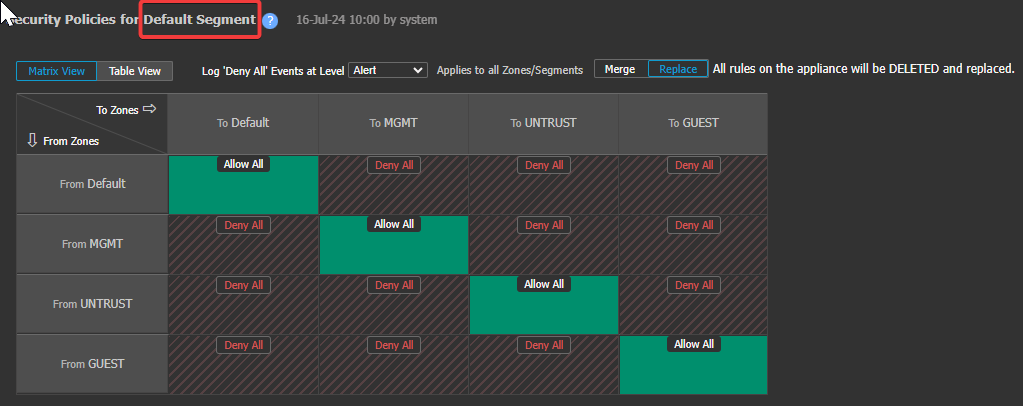
Security Policy applies Before the VRF/Segmentation policy and only works in default segment!
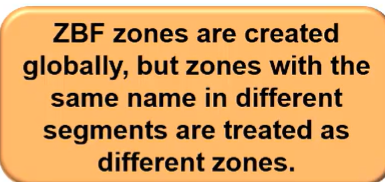
Templated ZBFW security policy is only active in the default segment, all other segment rules will have to go in the VRF section.
Updated 4 months ago
What’s Next
Did this page help you?